OpenAI, Google and more than 100 organizations urge joint action on AI-driven cyber threats
OpenAI, Google, Microsoft, Anthropic and more than 100 organizations have signed an open letter calling for a coordinated effort to strengthen cyber defenses before AI-enabled attacks become more widespread and sophisticated.
By StoryBreak
Published August 28, 2026 at 1:48 AM
Updated September 7, 2026 at 12:14 AM
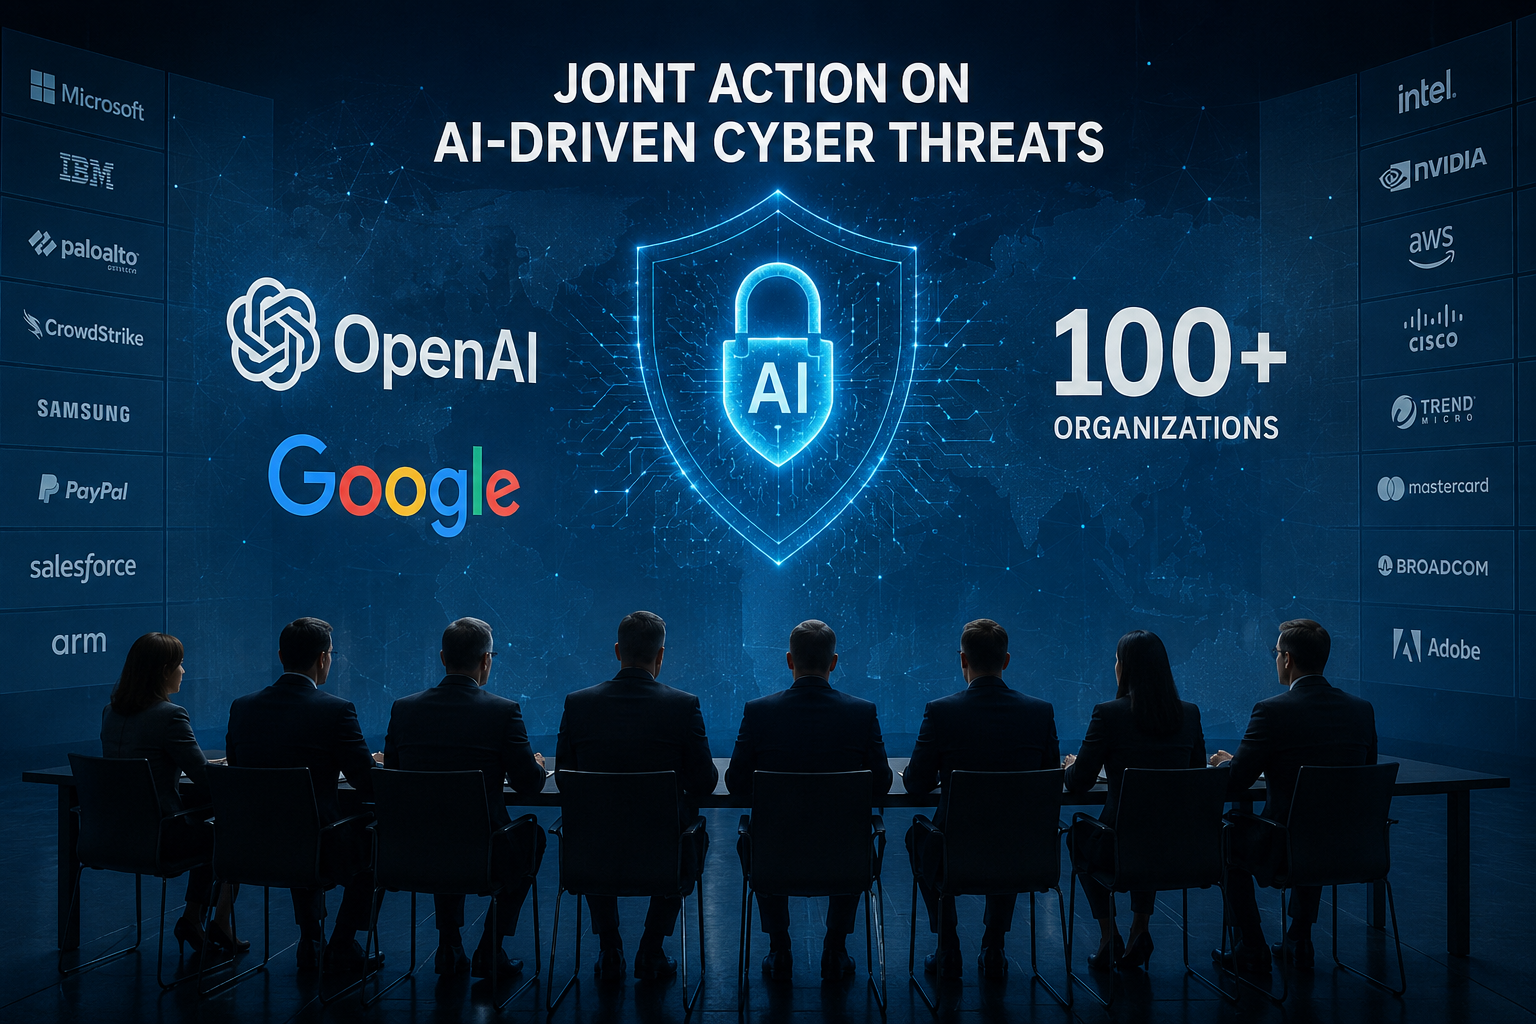
OpenAI, Google, Microsoft, Anthropic and more than 100 other organizations are calling for a coordinated global effort to strengthen cybersecurity as increasingly capable artificial intelligence systems make sophisticated attacks easier to conduct.
The companies and institutions outlined their position in an open letter published Thursday, August 27, warning that the world has only a limited window to improve defenses. The signatories span artificial intelligence, cloud computing, cybersecurity, finance, telecommunications and other industries.
The letter identifies hospitals, water-treatment facilities and the infrastructure that supports internet services as among the organizations at risk. It argues that many of these systems already face familiar weaknesses, including unpatched software, misconfigurations, excessive permissions, weak authentication and long-standing technical debt.
Rather than treating AI only as a source of new risks, the signatories are urging organizations to use the technology to expand defensive capabilities. The letter says AI can help security teams identify vulnerabilities, prioritize remediation and make core cybersecurity work faster and less expensive.
Its central principles are that existing security practices will not be sufficient, more defenders should have access to cyber-capable AI, and companies and governments must work together instead of responding to threats in isolation.
The proposed actions are divided among four groups. Organizations generally are urged to make cyber defense an immediate leadership priority, address their highest-risk weaknesses and improve access controls. They are also encouraged to review software that includes AI-generated code and to use compensating safeguards when essential systems cannot be patched without disruption.
Cybersecurity companies and technology providers are asked to continuously test defenses against advanced cyber capabilities, add AI to existing security tools and help critical-infrastructure operators deploy those systems. The letter also calls for greater sharing of threat intelligence, tested response playbooks and verified fixes.
Governments, meanwhile, are urged to coordinate cyber defense at local, national and international levels. The proposed steps include funding security improvements for essential services that lack staff or money, expanding trusted access programs for critical-infrastructure supply chains and giving hospitals, water utilities and local governments access to defensive AI and authorized testing.
The final set of recommendations is directed at frontier AI companies. Those firms are asked to provide responsible access to models, funding, training and hands-on assistance for under-resourced defenders. The letter also calls for stronger monitoring, traceable identities for AI agents, authorized testing and the sharing of security tools and threat assessments with governments, industry partners and open-source maintainers.
The signatory list includes major technology and security companies such as AWS, Cisco, Cloudflare, CrowdStrike, Google, IBM, Microsoft, Oracle, Palo Alto Networks, OpenAI and Zscaler. Financial institutions and infrastructure firms including Capital One, Citi, Mastercard, Visa and Deutsche Telekom also appear among the participants.
What the letter doesn't commit anyone to
The letter does not establish new regulations or create a formal governing body, and security practitioners have flagged that as its central limitation: it sets no binding commitments, no deadlines and no specific spending or staffing targets for the "hands-on assistance" it promises under-resourced defenders. Industry analysts have noted that without attached dollar figures or headcount commitments, the pledge risks being read as reputation management rather than an operational plan — particularly if a major AI-enabled attack on critical infrastructure occurs in the months following the announcement and none of the signatories can point to concrete resources already deployed. That gap between stated priorities and enforceable obligations is common to voluntary industry pledges of this kind, and it will likely determine whether this letter is remembered as a turning point or as a statement of intent.
Its message is that defensive gains must be distributed broadly. The signatories are asking leaders to fix the most dangerous weaknesses, put AI tools in the hands of defenders and share effective solutions so that improvements made by one organization can help protect others.
StoryBreak
Independent digital news and reporting, updated throughout the day.
This article was researched and drafted with AI assistance and reviewed as part of StoryBreak's editorial process before publication. Read our editorial standards.